ISO 27001 & ISO 42001 Certification Success Story: 24/7 AI Healthcare Receptionist
Quick summary: Borderless CS is an ISO 27001 consultant in Australia that helped 24/7 AI Healthcare Receptionist, an AI-powered healthcare technology company, achieve both ISO 27001 certification and ISO 42001 certification. The engagement covered a gap assessment, ISMS and AIMS implementation, risk assessment, policy development, and certification-readiness support resulting in two internationally recognised certifications and a stronger governance foundation across information security and AI risk management.
We help organisations strengthen information security, manage cyber risk and establish practical governance frameworks that support security, compliance and long-term business growth.
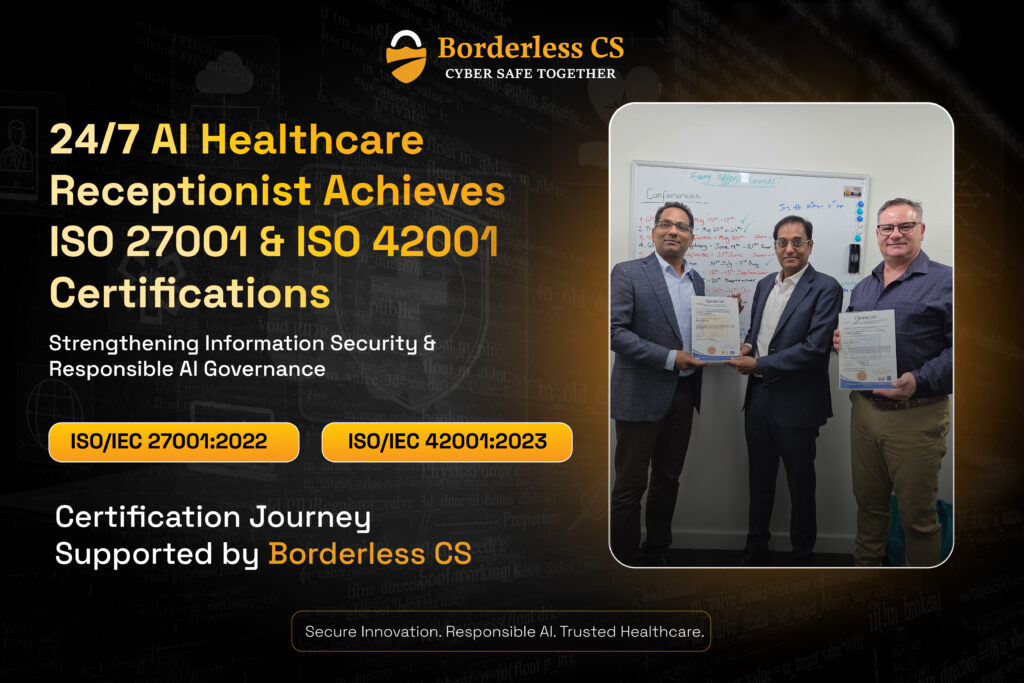
We are proud to share the success story of our client, 24/7 AI Healthcare Receptionist, and their achievement of ISO 27001 and ISO 42001 certifications.
As an AI-powered healthcare technology organisation, 24/7 AI Healthcare Receptionist operates in an environment where information security, data protection, AI governance and customer trust are critical.
Borderless CS worked closely with the client throughout their certification journey, supporting the implementation and strengthening of an Information Security Management System (ISMS) aligned with ISO/IEC 27001:2022 and an Artificial Intelligence Management System (AIMS) aligned with ISO/IEC 42001:2023.
The successful outcome represents more than achieving two internationally recognised certifications. It provides a stronger foundation for managing information security risks, strengthening AI governance and supporting responsible AI practices.
The Challenge: Securing an AI-Powered Healthcare Solution
Artificial intelligence is transforming the way organisations interact with customers and deliver services. In healthcare technology, this innovation also brings important considerations around security, data management, accountability and responsible use of AI.
For our client, the goal was clear: establish structured management systems that could strengthen both information security and AI governance while supporting the organisation’s continued growth.
This required addressing two closely connected areas:
ISO/IEC 27001:2022 – Information Security Management System (ISMS)
ISO/IEC 42001:2023 – Artificial Intelligence Management System (AIMS)
Rather than treating ISO certification as a documentation exercise, Borderless CS focused on helping the client establish practical processes that could become part of ongoing business operations.
Why ISO 27001 Certification?
ISO 27001 certification is internationally recognised as an important benchmark for information security management.
ISO/IEC 27001 provides requirements for establishing, implementing, maintaining and continually improving an Information Security Management System (ISMS).
An effective ISMS enables organisations to take a structured and risk-based approach to protecting information. (Reference: ISO.org – ISO/IEC 27001)
For technology and AI-driven organisations, ISO 27001 can help establish stronger governance across areas such as:
- Information security risk management
- Security policies and procedures
- Access control
- Asset management
- Supplier and third-party security
- Information security incident management
- Business continuity
- Security roles and responsibilities
- Monitoring and measurement
- Internal audit
- Management review
- Continual improvement
For organisations considering ISO 27001 certification in Australia, implementing an effective ISMS can also provide greater assurance to customers, business partners and other stakeholders that information security risks are being managed systematically.
How Borderless CS Supported the ISO 27001 Certification Journey
Every organisation has a different technology environment, risk profile and level of security maturity.
Our approach began by understanding the client’s existing environment before determining what needed to be strengthened.
ISO 27001 Gap Assessment
Borderless CS reviewed existing information security practices against the applicable requirements of ISO/IEC 27001:2022.
The ISO 27001 gap assessment helped identify existing strengths, potential gaps and areas requiring further development.
This provided a structured roadmap for progressing towards certification readiness.
Information Security Management System (ISMS)
A core part of the engagement involved strengthening the client’s Information Security Management System.
Borderless CS supported key areas including:
- ISMS scope
- Information security objectives
- Governance and responsibilities
- Information security policies
- Risk assessment
- Risk treatment
- Applicable security controls
- Monitoring and measurement
- Internal audit
- Management review
- Corrective actions
- Continual improvement
Our focus was on creating a management system that was practical and aligned with how the organisation operates.
Information Security Risk Assessment and Risk Treatment
Risk management is fundamental to ISO 27001.
Rather than implementing security controls simply to satisfy a checklist, organisations need to understand the risks relevant to their information, systems and business operations.
Borderless CS supported the client in establishing a structured approach to identifying, assessing and treating information security risks.
This enabled security decisions and controls to be considered within the context of actual organisational risks.
ISO 27001 Policies, Procedures and Governance
Documentation is an important component of ISO 27001 compliance and certification readiness, but effective policies should reflect real business practices.
Borderless CS supported the development and refinement of relevant policies, procedures, registers and governance documentation.
The objective was to ensure that documentation was clear, practical and maintainable while supporting the requirements of the ISMS.
Extending Governance with ISO 42001 Certification
As an AI-powered organisation, 24/7 AI Healthcare Receptionist also needed to consider risks and responsibilities extending beyond traditional information security.
Artificial intelligence introduces additional governance considerations around accountability, transparency, data, oversight and responsible use.
ISO/IEC 42001:2023 provides a structured framework for establishing, implementing, maintaining and continually improving an Artificial Intelligence Management System (AIMS).
By working towards ISO 42001 certification alongside ISO 27001, the client was able to strengthen both information security and AI governance through complementary management systems.
What Is ISO 42001 Certification?
ISO 42001 is an international management-system standard focused specifically on artificial intelligence.
It provides a framework for organisations developing, providing or using AI systems to manage AI-related risks and opportunities systematically.
An Artificial Intelligence Management System can support areas including:
- AI governance
- AI risk management
- Responsible AI
- AI policies and objectives
- Roles and accountability
- Data considerations
- Transparency
- Human oversight
- AI impact considerations
- Monitoring and measurement
- Continual improvement
For organisations increasingly integrating AI into products, services and business processes, establishing formal AI governance can help create greater accountability and consistency around how artificial intelligence is managed.
Building an Artificial Intelligence Management System (AIMS)
Borderless CS supported 24/7 AI Healthcare Receptionist in strengthening its Artificial Intelligence Management System and establishing governance processes aligned with ISO/IEC 42001.
The engagement considered areas such as AI governance, policies, responsibilities, risk management, monitoring and continual improvement.
This helped provide a structured approach for managing AI-related risks while complementing the organisation’s existing information security framework.
Integrating ISO 27001 and ISO 42001
One of the key advantages of implementing ISO 27001 and ISO 42001 together is the opportunity to align common management-system processes.
Both standards take a structured management-system approach, creating opportunities to integrate areas such as:
- Leadership and governance
- Policies and objectives
- Risk management
- Roles and responsibilities
- Competence and awareness
- Document management
- Monitoring and measurement
- Internal audits
- Management reviews
- Corrective actions
- Continual improvement
For 24/7 AI Healthcare Receptionist, this approach helped create a more cohesive governance environment connecting information security, cybersecurity risk, AI risk and responsible AI governance.
Internal Audit and Certification Readiness
Having policies and procedures alone is not enough for an effective ISO management system.
Organisations need to demonstrate that relevant processes are implemented, operating and continually reviewed.
Borderless CS supported the client’s certification-readiness activities, including preparation for internal audit and management review.
These activities helped identify areas requiring attention before independent certification assessment and provided greater confidence that the ISMS and AIMS were operating as intended.
The Outcome: ISO 27001 & ISO 42001 Certification Success
Following the implementation and certification journey, 24/7 AI Healthcare Receptionist achieved ISO 27001 and ISO 42001 certifications.
This represents an important milestone for our client and reflects their commitment to both information security and responsible AI governance.
More importantly, the engagement helped establish stronger foundations across:
- Information security management
- Cybersecurity risk management
- AI governance
- AI risk management
- Policies and procedures
- Organisational accountability
- Internal governance
- Monitoring and review
- Continual improvement
For Borderless CS, the successful outcome demonstrates the value of combining practical security implementation with structured governance and certification readiness.
Why ISO 27001 and ISO 42001 Work Well Together
ISO 27001 and ISO 42001 address different but increasingly interconnected areas.
ISO 27001 focuses on establishing and continually improving an Information Security Management System.
ISO 42001 focuses on establishing and continually improving an Artificial Intelligence Management System.
Together, they can provide organisations with a stronger governance foundation covering:
Information Security | Cybersecurity Risk | AI Governance | AI Risk Management | Responsible AI
This can be particularly relevant for AI companies, SaaS providers, healthcare technology organisations, software companies, cloud service providers and other organisations adopting artificial intelligence.
More Than ISO 27001 Compliance
Organisations often begin their ISO 27001 certification journey because of customer requirements, contracts, tenders or growing security expectations.
However, the value of an effective ISMS extends beyond certification.
A well-implemented Information Security Management System creates a repeatable framework for identifying risks, determining appropriate treatments, monitoring security performance and continually improving information security practices.
Similarly, ISO 42001 can help organisations move from informal AI practices towards a more structured approach to AI governance and AI risk management.
At Borderless CS, our focus is therefore not simply on preparing documentation for an audit. We help organisations establish practical governance frameworks designed to continue delivering value after certification.
Related: organisations pursuing ISO 27001 often pair certification with regular penetration testing to satisfy Annex A control requirements.
ISO 27001 Consulting Services in Australia
If your organisation is considering ISO 27001 certification in Australia, Borderless CS can support you throughout your certification-readiness journey.
Our ISO 27001 consulting services can support organisations across areas including:
- ISO 27001 gap assessment
- ISO 27001 readiness assessment
- ISMS implementation
- Information security risk assessment
- Risk treatment planning
- ISO 27001 policies and procedures
- ISO 27001 documentation
- Internal audit
- Management review preparation
- Certification readiness
- Continual improvement
We work closely with organisations to understand their business, technology environment and security risks before developing an approach aligned with their requirements.
ISO 42001 Consulting & AI Governance
For organisations developing, providing or using artificial intelligence, Borderless CS can also support ISO 42001 certification readiness and AI governance.
Our services can support areas including:
- ISO 42001 gap assessment
- Artificial Intelligence Management System implementation
- AI governance
- AI risk assessment
- Responsible AI frameworks
- AI policies and procedures
- Roles and accountability
- Internal audit
- ISO 42001 certification readiness
- Integration of ISO 27001 and ISO 42001
An integrated approach can be particularly valuable for organisations that need to manage both information security and AI-related risks without creating unnecessary duplication.
Looking for an ISO 27001 Consultant in Australia?
Choosing the right ISO 27001 consultant can help make the certification journey more structured and manageable.
Borderless CS works with organisations to identify gaps, understand risks, establish practical management systems and prepare for independent certification assessment.
For AI-driven organisations, our approach can also bring together ISO 27001, ISO 42001, information security and responsible AI governance.
The successful certification journey of our client, 24/7 AI Healthcare Receptionist, demonstrates how these frameworks can work together to strengthen security, governance and organisational trust.
Start Your ISO Certification Journey with Borderless CS
Whether you’re starting your ISO 27001 certification journey, improving an existing ISMS, preparing for ISO 42001 certification, or strengthening your organisation’s AI governance, Borderless CS can support you from initial assessment through to certification readiness.
Our approach focuses on practical implementation, effective risk management and governance frameworks that continue delivering value beyond the certification audit.
Strengthen Information Security. Build Responsible AI Governance. Prepare for Certification with Confidence.
Talk to Borderless CS about your ISO 27001 and ISO 42001 requirements today.
This article was reviewed by cybersecurity professionals experienced in penetration testing, compliance frameworks, and Australian cyber security regulations.
Frequently Asked Questions
1. What is ISO 27001 certification?
ISO 27001 certification demonstrates that an organisation has established an Information Security Management System (ISMS) aligned with ISO/IEC 27001 requirements. The framework helps organisations systematically identify, assess and manage information security risks while continually improving their security practices.
2.What are the benefits of ISO 27001 certification in Australia?
ISO 27001 certification can help Australian organisations strengthen information security governance, improve risk management, establish consistent security processes and provide greater assurance to customers and stakeholders. It may also help organisations respond to customer security requirements, supplier assessments and tender requirements
3. What is ISO 42001 certification?
ISO 42001 certification relates to an organisation’s Artificial Intelligence Management System (AIMS). ISO/IEC 42001 provides a structured framework for organisations developing, providing or using AI systems to manage AI-related risks, opportunities, responsibilities and governance.
4. What is the difference between ISO 27001 and ISO 42001?
ISO 27001 focuses on information security management, while ISO 42001 focuses on artificial intelligence management and AI governance.
ISO 27001 helps organisations establish an Information Security Management System (ISMS), whereas ISO 42001 provides the framework for an Artificial Intelligence Management System (AIMS).
For AI-driven organisations, implementing both standards can provide a more comprehensive approach to information security, AI risk management and responsible AI governance.
5. Can ISO 27001 and ISO 42001 be implemented together?
Yes. ISO 27001 and ISO 42001 can be implemented using an integrated management-system approach. The standards share common management principles across areas such as governance, risk management, policies, roles and responsibilities, internal audits, management reviews and continual improvement.
An integrated approach can help reduce unnecessary duplication while strengthening both information security and AI governance.
6. Why is ISO 42001 important for AI companies?
Organisations developing or using artificial intelligence face risks and governance considerations that extend beyond traditional cybersecurity.
ISO 42001 provides a structured framework for areas such as AI governance, AI risk management, accountability, transparency, responsible AI and continual improvement. This can help organisations establish clearer processes for managing AI systems and their associated risks.
7. Who issues ISO 27001 and ISO 42001 certification?
ISO does not directly certify organisations. Certification is conducted by an independent certification body that assesses whether the organisation’s management system meets the applicable standard requirements.
An ISO 27001 or ISO 42001 consultant, such as Borderless CS, can support implementation, gap assessment, internal audit and certification readiness ahead of the independent certification assessment.
8. How long does ISO 27001 certification take?
The timeframe for ISO 27001 certification varies depending on factors such as the organisation’s size, scope, existing security maturity, complexity, available documentation and readiness.
An initial ISO 27001 gap assessment can help identify the work required and provide a clearer implementation roadmap before the organisation proceeds to an independent certification audit.