
Penetration Testing for Compliance in Australia
Penetration Testing for Compliance in Australia Every few weeks someone calls us holding a penetration test report that cost them
Reviewed by Jaya Prakash (JP) Muthusamy, Founder and CEO of Borderless CS and Board Director, CREST ANZ | Updated October 2026
Borderless CS is a CREST accredited penetration testing company, accredited by both CREST ANZ and CREST International. Our CREST and OSCP certified testers deliver manual web application, API, network, cloud and mobile penetration testing for Australian organisations, with fixed quotes and free retesting.

The facts buyers and auditors ask for first
CREST ANZ and CREST International, for penetration testing
Led by a CREST ANZ Board Director
CREST CRT, OffSec OSCP and OSEP, EC-Council CEH
Web, API, network, cloud, mobile, wireless, AI and SaaS
From $3,500 for a single web application, fixed quote
2 to 4 weeks from kick-off to final report
Risk-rated report, debrief, free retest, Letter of Attestation
ISO 27001:2022 certified and SOC 2 Type II
CREST is an international not-for-profit accreditation and certification body for the cyber security industry. A CREST accredited penetration testing company has been independently assessed on its testing methodology, quality processes, data handling and the competence of its testers.
Accreditation is not a one-off badge. Members resubmit their policies and procedures to CREST every year, sign the CREST Code of Conduct annually and can face a full re-assessment every three years. Buyers also get access to CREST’s formal complaints process if something goes wrong.
When you choose a CREST accredited provider, you are not relying on the provider’s own claims. CREST has already checked how the company scopes, tests, protects your data and reports.
New to penetration testing? Read our guide to penetration testing services in Australia.

Many buyers and regulators expect independent, accredited testing. These are the most common reasons Australian organisations choose a CREST provider.
Tenders and supplier panels often list CREST accreditation as a requirement or a scored criterion.
APRA CPS 234 expects systematic, independent testing of security controls.
Practice software partner programs ask for independent testing. We support Best Practice Software partner approval.
Security questionnaires and cyber insurance renewals ask for a recent report from a recognised provider.
| What you get | Non-accredited provider | CREST accredited (Borderless CS) |
|---|---|---|
| Independent check of the company | Self-declared | Policies and processes assessed by CREST |
| Testing methodology | Varies, rarely reviewed | Documented and assessed |
| Tester competence | Depends on the individual | CREST CRT and OffSec OSCP certified testers |
| Handling of your data | Unknown | Assessed by CREST, plus ISO 27001 and SOC 2 Type II |
| Code of conduct | None | CREST Code of Conduct, signed every year |
| If something goes wrong | Your contract only | CREST complaints and resolution process |
| Accepted by auditors and tenders | Sometimes questioned | Widely recognised |
Any provider can put a logo on its website. Take two minutes to check.
Look up the company name on CREST's official supplier directory.
Confirm the listing covers penetration testing, and ANZ or International.
Request the certifications of the testers on your job, such as CRT or OSCP.
A good report has an executive summary, evidence and clear fixes.
Retesting proves your fixes worked. Ours is included.


Accreditation covers the company. Certification covers the person. Our engagements are led by testers who have passed hands-on, independently assessed exams, including CREST CRT and OffSec OSCP and OSEP.
Our practice is led by our Founder and CEO, Jaya Prakash (JP) Muthusamy, who is also a Board Director of CREST ANZ, so our methodology keeps pace with how CREST expects testing to be done.
CREST ANZ
CREST ANZ CEO George Bej said the accreditation shows “a strong commitment to technical competence, professional integrity and the quality of its service delivery.”
Read the CREST ANZ announcementCREST INTERNATIONAL
Announced by CREST International in August 2026, following an assessment of our operating procedures, personnel security, data protection and testing methodologies.
Read the CREST International announcementEvery service below is delivered under our CREST accreditation, by certified testers.
Logins, roles, sessions and business logic tested against the OWASP Top 10 and beyond.
REST and GraphQL APIs tested for broken authorisation, data exposure and abuse.
Internet-facing systems, VPNs and remote access, the first doors attackers try.
What an attacker could reach from inside, including Active Directory and lateral movement.
iOS and Android apps, local data storage and the APIs behind them.
Azure and AWS identity, storage and configuration weaknesses.
Wi-Fi security, guest isolation and rogue access points.
Manual review of code for flaws that testing alone can miss.
Prompt injection, data leakage and access control in AI-enabled products.
Ongoing monitoring and expert review between scheduled tests.
Tenant isolation and access control between customers.
Testing that supports Best Practice Software partner integration approval.
The same six steps on every engagement, from scoping to a Letter of Attestation.
We discuss your environment, testing requirements and objectives to agree on a clear scope before testing begins.
Our team gathers relevant information about the target environment to understand the attack surface and identify potential entry points.
Our consultants manually assess your systems and applications to uncover security weaknesses that automated tools may miss.
Where appropriate, identified vulnerabilities are safely tested to understand whether they can be exploited and what impact they could have.
We assess the findings, explain the risks and provide a clear report with evidence and practical recommendations for remediation.
Once fixes are applied, we retest the identified vulnerabilities to confirm they have been properly addressed.
CREST accredited testing does not have to cost more. A single web application test with Borderless CS starts from $3,500 (AUD, ex GST), and every engagement gets a fixed quote after a free scoping call. Retesting is always included.
| Test type | From (AUD, ex GST) |
|---|---|
| Web application | $3,500 |
| API | $3,500 |
| External network | $3,500 |
| Internal network | $3,500 |
| Cloud (Azure or AWS) | $3,500 |
| Mobile app (iOS or Android) | $3,500 |
| Retesting | Included |
We provide penetration testing Australia-wide, and local testers mean on-site testing, face-to-face debriefs and people who understand your industry and state requirements.
Penetration Testing for Compliance in Australia Every few weeks someone calls us holding a penetration test report that cost them

Top 10 CREST-Accredited Penetration Testing Companies in Australia (Sep 2026) If your organisation is buying penetration testing for a tender,
What Is Penetration Testing? A Complete Guide for Australian Businesses If you’re searching for what is penetration testing, you’re likely
Real engagements across government, healthcare and technology. Each story covers the scope, what we found and what changed.
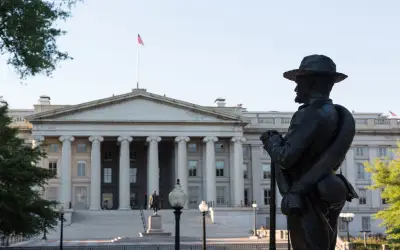
Government: Brimbank City Council Penetration testing of a critical web application supporting citizen portals, online payments and internal services, with a clear remediation roadmap

24/7 AI Healthcare Receptionist Grey-box web application and API testing that helped the platform meet the security requirements for Best Practice Software partner approval, alongside Cybercert Gold SMB1001 Level 3 certification.

Independent CREST-accredited penetration testing of Zalamar Tech’s applications and infrastructure, covering authentication, access control and injection risks, with prioritised remediation guidance for its technology services.
CREST accredited penetration testing is a penetration test delivered by a company that CREST has assessed and accredited for penetration testing services. CREST checks the company’s testing methodology, quality processes, data handling and staff competence, and the company must sign the CREST Code of Conduct every year. It gives buyers independent assurance instead of relying on the provider’s own claims.
Yes. Borderless CS is accredited for penetration testing by both CREST ANZ and CREST International. You can verify this yourself on the CREST Marketplace, CREST’s official supplier directory. Both accreditations were publicly announced by CREST ANZ and CREST International, and our Founder and CEO, Jaya Prakash (JP) Muthusamy, is a Board Director of CREST ANZ.
CREST International is the global not-for-profit body that sets the standards and runs accreditation and certification. CREST ANZ represents CREST members in Australia and New Zealand and works with local industry and government. Holding both means our accreditation is recognised by Australian buyers and by organisations overseas.
Search the company name on the CREST Marketplace at marketplace.crest.org and check that the listing covers penetration testing in your region. Then ask the provider which certified testers will work on your job and request a sample report. A logo on a website is not proof on its own.
Accreditation applies to the company and covers how it scopes, tests, protects data and reports. Certification applies to individual testers who pass CREST exams, such as CPSA, CRT and CCT. The strongest choice is an accredited company whose engagements are led by certified testers, which is how Borderless CS works.
CRT stands for CREST Registered Penetration Tester. It is a practical exam taken in a controlled lab, covering infrastructure and web application testing, and candidates must already hold the CREST CPSA. CREST positions it for testers with around three years of hands-on experience.
CREST members resubmit their policies, processes and procedures every year and sign the Code of Conduct annually. CREST can also carry out a full re-assessment every three years to confirm standards are still being met.
It depends on who is asking for the test. Government tenders, financial services, healthcare software partner programs, enterprise customers and cyber insurers often expect testing by an accredited provider. If a contract, auditor or regulator asks for independent testing, a CREST accredited report is the safest evidence to provide.
Not with us. Web application, API and external network tests with Borderless CS start from $3,500 (AUD, ex GST), and retesting is included. Every engagement gets a fixed quote after a free scoping call, so there are no surprises.
Most engagements take 2 to 4 weeks from kick-off to final report. Active testing usually takes 2 to 8 days depending on the scope, for example 3 to 5 days for a single web application or API and 4 to 8 days for an internal network.
You receive an executive summary for leadership, a detailed technical report with risk-rated findings, evidence and prioritised fixes, and a debrief with our testers. After you fix the issues we retest them at no extra cost and issue a Letter of Attestation you can share with customers, auditors, insurers and tender panels.
Yes. Our reports are used as evidence for ISO 27001, SOC 2, PCI DSS v4.0.1 requirement 11.4, APRA CPS 234, the Essential Eight, the SOCI Act and Best Practice Software partner approval. We can map findings to the framework you name, so your auditor sees exactly what was tested.
Don’t wait for an attacker to discover your vulnerabilities first.
Talk to Borderless CS about your applications, infrastructure and security requirements, and we’ll help you determine the appropriate CREST accredited penetration testing scope for your organisation.
Contact Borderless CS today for a free consultation and tailored security roadmap.
100% Cybersecurity Focused Company
Free 30 Min Cybersecurity Consultation for Your Business
As a Leading Cybersecurity Company in Australia, we are offering a free 30-minute cybersecurity consultation to help evaluate potential vulnerabilities in your digital environment.